Home Blog Page 35

Zilliqa Halts Native Transactions After Ledger App Flaw Exposes Private Keys – NFT Plazas Zilliqa Halts Native Transactions After Ledger App Flaw Exposes Private Keys

0
Zilliqa Halts Native Transactions After Ledger App Flaw Exposes Private Keys – NFT Plazas Zilliqa Halts Native Transactions After Ledger App Flaw Exposes Private Keys


Zilliqa has halted native ZIL transactions following the discovery of a critical vulnerability in the network’s Ledger application, which allows the private keys of certain accounts to be recovered from public signatures on the blockchain. The incident was disclosed after an undisclosed amount of ZIL was stolen from an exchange partner’s cold wallet, forcing the project to request centralized platforms to pause ZIL deposits and withdrawals to curb the movement of funds. 

According to Zilliqa, the flaw lies in the native transaction signing process using the Ledger app and does not affect EVM transactions or official SDKs. The project stated that the vulnerability had existed in app versions dating back to 2019, with on-chain exploitation signs detected on July 19, 2026, two days before the root cause was isolated.

Exchange Theft and Initial Response

Zilliqa publicly disclosed the incident on July 20, stating that an undisclosed amount of ZIL had been stolen from an exchange partner’s cold wallet. At the time, the project did not specify the technical cause or the scale of damages, noting that an investigation was ongoing to determine the root cause and the scope of impact.

Exchanges were subsequently notified and requested to pause ZIL deposits and withdrawals as a precautionary measure to prevent the stolen funds from being transferred or sold through centralized platforms while the verification process continued. 

On July 21, Zilliqa updated that it found no evidence suggesting the incident originated from wallet management procedures or operational activities of the exchange. The investigation then shifted to a technical issue affecting transaction signing in a group of legacy ZIL1 wallets, before the project disclosed detailed information about the vulnerability in the Zilliqa Ledger app a day later.

Affected Wallets and Transaction Scope

Zilliqa limited the scope of impact to private keys that had been used to sign native Zilliqa transactions via a Ledger device. According to the project’s advisory, accounts that have broadcast approximately 5 or more native transactions using the Zilliqa Ledger app should be considered compromised. 

This risk applies to signatures already publicly recorded on-chain, meaning subsequent software updates cannot reverse the exposure level of affected private keys. Users with accounts in this group must stop using the compromised keys, rather than merely updating the transaction-signing app. 

EVM transactions are unaffected, while transactions signed through official SDKs such as zilliqa-js, gozilliqa-sdk, and pyzil are also outside the scope of the flaw. The incident is therefore isolated to the native signing path of the Zilliqa Ledger app. 

Zilliqa has not disclosed the amount of ZIL stolen, the number of affected accounts, or the total value of assets held in vulnerable addresses. As a result, the overall financial extent of the incident remains unclear.

Ledger App Vulnerability

The root cause lies in how the Zilliqa Ledger app generates nonces for EC-Schnorr signatures on the secp256k1 curve. For each signature, the app needs to generate a fresh, random, and unpredictable 256-bit nonce; if the nonce is biased or lacks entropy, multiple signatures can expose the private key. 

The app’s signing routine generates 40 bytes of randomness and then reduces this value modulo the order of the curve to produce a 256-bit number. However, when copying the result into the nonce buffer, the code mistakenly extracted 32 bytes from the 40-byte output, retaining 8 bytes of zero-padding while discarding 8 bytes of entropy. 

This flaw leaves the 64 most significant bits of each nonce fixed at zero. With approximately 5 or more affected signatures, the private key can be recovered in seconds on commodity hardware using Hidden Number Problem solving and lattice reduction techniques.

Native Transaction Halt

Zilliqa halted native non-EVM transactions as a protective measure while finalizing a remediation plan. The move aims to prevent further asset losses from vulnerable accounts while restricting the movement of stolen ZIL through the native transaction flow. 

Affected accounts cannot be protected by a standard transfer transaction either. If a private key can already be recovered from on-chain data, an attacker holding the same key can detect and front-run the user’s asset transfer transaction. Therefore, attempting to move funds independently may be ineffective and increase risk, while EVM transactions continue to remain unaffected.

Remediation Plan and User Guidance

A fixed build of the Ledger app is being prepared in coordination with Ledger. This fix will restore the full nonce generation process to prevent the app from creating further weakened signatures in the future. However, the patch cannot reverse the risk for private keys that have already signed the required number of affected native transactions previously. 

Keys belonging to the affected group ultimately need to be retired from use. Zilliqa is finalizing a remediation plan to safeguard balances in associated accounts and will publish separate instructions for users who have signed native Zilliqa transactions using Ledger. Until official guidance is provided, users are advised not to act independently and to monitor only the project’s official channels. 

KuCoin was credited by Zilliqa for assisting in identifying the root cause within the Ledger app’s nonce generation process, recovering affected private keys from on-chain data, and confirming ongoing exploitation activity. However, Zilliqa has not publicly confirmed whether KuCoin was the exchange partner that lost ZIL in the initial announcement.


Source link

AFX Trade Bridge Exploit Drains $24.15M USDC on Arbitrum – NFT Plazas AFX Trade Bridge Exploit Drains $24.15M USDC on Arbitrum

    0
    AFX Trade Bridge Exploit Drains .15M USDC on Arbitrum – NFT Plazas AFX Trade Bridge Exploit Drains .15M USDC on Arbitrum


    AFX Trade has paused its Arbitrum-operated USDC custody bridge after approximately $24.15 million in USDC was drained on July 22, 2026, according to a Blockaid alert. The incident was detected at 21:30 UTC, targeting AFX’s bridge infrastructure rather than Arbitrum’s native bridge. The exact root cause remains under investigation by the project, while security firms monitor the flow of stolen funds to support recovery efforts.

    AFX Pauses Bridge After $24.15M USDC Drain

    AFX confirmed an incident involving its AFX-operated USDC custody bridge on Arbitrum, which handles USDC deposits/withdrawals for the project’s trading ecosystem. Immediately upon detecting the incident, AFX stated it paused bridge operations and activated its incident response procedures.

    Initial assessments indicate the incident appears isolated to the project-operated custody bridge. AFX stated that its trading infrastructure, AFX mainnet, and the Arbitrum network were not compromised.

    Offchain Labs shared a similar message. Steven Goldfeder, co-founder and CEO of Offchain Labs, stated that the relevant transaction originated from a third-party protocol, while Arbitrum’s native bridge was neither hacked nor exploited. This information further indicates that the damage was concentrated on AFX’s bridge, though the scale of the loss for the project remains substantial.

    Funds Flow to Ethereum

    Blockaid reported that the exploit was detected at 21:30 UTC on July 22, 2026, with approximately $24.15 million in USDC drained from the AFX-operated bridge. This figure almost matches AFX Bridge’s pre-incident TVL. DefiLlama data logged AFX Bridge with around $24.18 million in TVL, all situated on Arbitrum, representing nearly the entirety of the locked assets in the bridge.

    After draining the USDC, the attacker transferred the assets from Arbitrum to Ethereum. PeckShield tracked the funds flow, noting that the stolen USDC was subsequently swapped into approximately 12,467.5 ETH. This ETH was traced back to wallet 0x6276…ebAC.

    Attacker wallet holding swapped ETH

    Attacker wallet holding swapped ETH. Source: PeckShield

    USDC is a stablecoin issued by Circle and can be frozen at the token contract level under certain circumstances. ETH lacks a similar mechanism, so once assets are swapped and consolidated into an Ethereum wallet, recovery relies more heavily on on-chain monitoring and exchange coordination.

    AFX Works to Recover Funds

    AFX stated it is working with blockchain security partners as the investigation continues. Meanwhile, SlowMist noted that the stolen funds remain in the attacker’s address, which has been reported to the Crypto Defense Alliance (CDA)—a collaborative network of exchanges and ecosystem partners. AFX said the associated address is being monitored by ecosystem stakeholders.

    The project also mentioned that Zellic, the firm that previously audited the bridge code, has been invited to assist in the investigation. A technical postmortem from AFX and security firms will serve as the basis to determine whether the incident involved code vulnerabilities, validator setup, key management, or backend signing flows.

    In parallel with the investigation, AFX amplified a white-hat settlement offer from Ken / Supercube, Head of Growth at AFX. The offer requests the party responsible for the bridge incident to return 70% of the stolen assets to address 0x222B…9f1B, while retaining the remaining 30% as a white-hat bounty.

    AFX’s recovery messaging currently focuses on two objectives: protecting the community and maximizing the potential recovery of user assets. However, at the time of writing, there is no public confirmation that any portion of the stolen funds has been returned.

    Root Cause Still Under Investigation

    AFX has not yet announced the final attack vector. In official updates, the project only stated that the investigation is ongoing and that further information will be provided as verified data becomes available. Therefore, there is currently no basis for a definitive conclusion on whether this was a smart contract exploit or a validator key compromise, beyond assessments from security sources.

    Nevertheless, several security sources and DeFi data aggregators have categorized the event as an infrastructure incident. SlowMist described it as an exploit targeting AFX’s cross-chain/USDC custody bridge on Arbitrum, suggesting the attacker used compromised validator hot keys to achieve a payout quorum. The DefiLlama Hacks database also recorded a $24.15 million loss for AFX Bridge, classifying it as “Infrastructure” with the technique labeled “Private Key Compromised.”

    If the postmortem confirms this classification, the AFX incident will serve as another example of operational risks at the bridge layer, including signing keys, validator setups, custody processes, and withdrawal verification mechanisms. Bridges typically hold large asset volumes in contracts or custody layers, making procedural flaws in verification capable of causing concentrated losses.

    AFX has not disclosed the number of affected keys or validators, the specific role of the bridge code, or user reimbursement plans. The project has also not confirmed any recovery from the stolen funds. The final technical root cause remains pending verification from AFX and investigative teams.


    Source link

    US Senate Republicans Release Updated Clarity Act Draft With New Ethics Package – NFT Plazas

    0
    US Senate Republicans Release Updated Clarity Act Draft With New Ethics Package – NFT Plazas


    Senate Republicans on Wednesday released an updated draft of the Digital Asset Market Clarity Act, unveiling a long-awaited ethics package negotiated with the White House just as lawmakers race to bring the crypto market structure bill to a floor vote before the August recess. The new text merges language from the Senate Banking and Agriculture Committees and, for the first time, includes conflict-of-interest rules covering the president and other senior officials, a provision Democrats have demanded for more than a year.

    US Senate Republicans released new crypto Clarity Act draft bill

    US Senate Republicans released new crypto Clarity Act draft bill

    What the ethics package does

    The revised bill would bar the president, vice president, members of Congress, federal judges, and other covered officials, along with their spouses, from issuing or sponsoring a digital asset for compensation while in office. Covered officials would be required to either sell their crypto holdings and any stakes in crypto-related companies, place those assets in a blind trust they do not control, or both, following procedures modeled on existing federal ethics-agreement rules. The restrictions would sunset at noon on January 20, 2029, meaning no penalties could apply to conduct occurring after that date.

    Enforcement would fall to the Department of Justice, which would gain civil authority to sue officials who knowingly violate the rules, as well as exchanges that knowingly list tokens issued in violation of the provision. Violators could be forced to surrender profits and pay civil penalties, and officials would need to disclose crypto sales exceeding $1,000. The Government Accountability Office would study whether additional ethics safeguards are needed.

    The draft explicitly excludes state attorneys general from bringing enforcement actions, specifying that only the U.S. Attorney General may sue under the section. It also preserves a separate carve-out allowing continued commercial use of an official’s name, image, or likeness if an issuer had already used it before that person entered covered status.

    Beyond the ethics language, the draft retains the Blockchain Regulatory Certainty Act, which would keep non-custodial software developers from being classified as money transmitters, and adds a new section aimed at bolstering law enforcement’s ability to pursue crypto-related crime, including expanded funding for blockchain investigations, training, and a new cyber center focused on threats from countries such as North Korea and Iran. Stablecoin issuers would be required to comply with lawful orders to freeze, seize, burn, and reissue tokens, and the bill outlines how customer assets would be treated separately from a company’s estate in the event of an exchange or custodian bankruptcy.

    Political reaction splits along familiar lines

    The White House approved the ethics language on July 21, following talks between Republican senators, including Wyoming’s Cynthia Lummis and Ohio’s Bernie Moreno, and administration officials. Lummis called it one of the most comprehensive ethics provisions ever attached to legislation and urged the Senate to pass the bill without delay. Digital Chamber CEO Cody Carbone called the draft a meaningful step toward a floor vote.

    Democrats were far less receptive. Seven Democratic senators, including Catherine Cortez Masto, Angela Alsobrooks, Cory Booker, Ruben Gallego, John Hickenlooper, Mark Warner, and Raphael Warnock, issued a joint statement saying the text falls short on ethics, consumer protection, illicit finance, and conflicts of interest. Alsobrooks, one of two Democrats who backed the bill in committee, called the DOJ-only enforcement structure “an unserious offer” and said she would not support the bill with that language, though Democrats intend to keep negotiating. Gallego voiced similar concerns, arguing the text still leaves loopholes for officials’ crypto dealings.

    Political reaction splits along familiar lines (Source: Eleanor Terrett’s X)Political reaction splits along familiar lines (Source: Eleanor Terrett’s X)

    Political reaction splits along familiar lines (Source: Eleanor Terrett’s X)

    The enforcement dispute carries particular weight given President Trump’s crypto holdings. Financial disclosures showed Trump earned more than $1 billion from crypto ventures last year, with roughly $580 million tied to World Liberty Financial, a venture co-founded by Trump family members that issues the WLFI token and USD1 stablecoin. Banking trade groups also flagged the draft’s stablecoin-yield provisions, saying the language still risks local lending activity.

    What the underlying bill still does

    Beyond the ethics fight, the Clarity Act remains an attempt to give the industry a regulatory rulebook by dividing oversight between the SEC and CFTC. The legislation would classify tokens, set registration and disclosure rules for exchanges, and direct regulators to build a pathway for tokenized securities and futures trading on public blockchains. Solana Policy Institute CEO Miller Whitehouse-Levine said the bill would offer clearer treatment for token fundraising and stronger consumer protections, while banking trade groups continue to push back on the draft’s stablecoin-yield language.

    A narrowing timeline

    The bill has already cleared major hurdles. The House passed its own version, H.R. 3633, 294-134 in July 2025. The Senate Banking Committee advanced its version 15-9 in May, with two Democrats joining Republicans, while the Agriculture Committee passed its companion measure covering CFTC jurisdiction earlier in the year. Majority Leader John Thune has signaled he intends to bring the merged bill to the floor as soon as next week regardless of Democratic support, though passage still requires 60 votes.

    The Senate has only a handful of working days left before the August recess, widely seen as the last realistic window to pass the bill in 2026 before focus shifts to the midterms. Prediction markets tracking the bill’s odds of becoming law this year have slid into the low-to-mid 30s percent range since the draft’s release, reflecting doubt over whether the remaining gap can close in time.


    Source link

    Palworld: Dog Coin Farming Guide

    Palworld: Dog Coin Farming Guide


    There are a few different currencies in Palworld, but arguably none more vital to the endgame than Dog Coins.

    Chances are you’ve found quite a few of these throughout your adventures, whether from fishing or simply scavenging through piles of scrap. However, one of the best ways to get a ton of these is by defeating or catching wild Mimog.

    Related

    Palworld: How to Get the Mimog Effigy

    Capturing Pals at a breakneck pace!

    Of course, if you’ve ever encountered a Mimog, you’ll be more than aware of how devious these little pups can be, running away from you at ridiculously high speeds if you don’t snare them quickly enough.

    So where can we consistently find Mimog, and how can we start hoarding those sweet Dog Coins? Let’s take a look!

    This is a late-game farming method, only available to those who have entered the World Tree.

    Preparing Your Party

    Palworld Katress Shot

    Before we go out to hunt down some Mimog, we first need to understand a little bit more about Pal types, partner skills, and drop rates.

    Mimog is a neutral-type Pal, and drops a random amount of Dog Coins every time it’s defeated. Luckily for us, there are a couple of Pals in the game that increase the quantity of items dropped by neutral Pals:

    Firstly, you’ll want to grab yourself a Katress, which can be found pretty early on around Mount Flopie, the Frostbound Mountains and No Man’s Trail. This will increase neutral-type drop rates by 40%. In addition, you’ll also have a chance to save a Pal sphere when thrown!

    Next up, you’ll need to find a Blazehowl Noct, which is found very commonly around Mount Obsidian. This will give you another 40% Neutral-type drop rate increase.

    Palworld Neutral Drops

    While it says this buff doesn’t stack, that only applies to stacking with the same species of Pal. Because we have 2 different species with 2 buffs, they can stack together.

    The next thing we will need to do is increase the star level of both of these Pals to level 4. You can do this either by catching a bunch of the same Pal and then condensing them through the Pal Condenser. Or you can simply use Starfruits, earned from Bounty Officers, the Relic Recycler, or bought from the Medal Merchant.

    When increased to the max level of 4, the drop rate will double to 80%, giving us a total of 160% increased drop rate for Dog Coins.

    Farming Mimog

    Spawning Locations

    Palworld Mimog Found

    Alright, so now you’ve got a 4-star Katress and Blazehowl Noct. They might take a while to get to 4-stars, but it will be well worth it in the long run.

    Now, you’ll need to head over to the World Tree, making sure you have a fast-flying Mount. Something like Jetragon or Eidrolon with strong moves is perfect for this.

    Mimog spawns more commonly in the World Tree compared to other places across the game. It isn’t confirmed whether Mimog spawns more commonly in specific biomes, but I’ve had pretty good results farming in the icy Northwest area.

    Firstly, you’ll want to start off from the Abandoned Lab fast-travel point, and then head in a straight line all the way to the Remnant Riverside fast-travel point. This is pretty much a straight line with a lot of open ground to cover, which seems to be good for spawning Mimog.

    Method and Drops

    Palworld Mimog Route

    Fly back and forth from these two points, keeping an eye out for the cyan-black of the Mimog as you zip on by. The quicker you can refresh the spawn radius of Pals, the more chances you have of finding a Mimog, so using a Pal with speed passives like Dimensional Leap is great here.

    As soon as you spot a Mimog, smack it with your hardest-hitting attack. Something like Meteorain is perfect here, as if the first meteor doesn’t kill, the spreading rings will catch the Mimog as it tries to flee. Make sure to mark the Mimog using the targeting mechanic, in case you lose sight of it!

    Palworld Meteor Mimog

    With all the drop rate modifiers, I’ve been getting anywhere from 300-600 Dog Coins every time I kill a Mimog, which honestly is pretty great for a very relaxed method.

    If you really want, you can alter the world settings in the main menu, upping the spawn rate to 3x. Now, instead of finding a single Mimog, you will find 3 sitting next to each other. However, this trivialises a lot of aspects of the game and may ruin your own immersion. Of course, whichever settings players enjoy the most should be prioritised.

    The Medal Merchant

    Palworld Dog Coin Shop

    So, you’ve been farming for a little while, and you’ve got a healthy stack of Dog Coins. What can we use these for, and why are they so valuable? Well, if you’ve visited any of the ruined churches around the map, you might have found a Medal merchant hanging around.

    These merchants have some of the most insane and broken items that you can use to create some incredibly overpowered pals. Here’s a quick look at some of your options:

    Item

    Cost

    Description

    Stat Fruits

    200

    These fruits will increase the hidden stat of a Pal by 10. Using the Ability Glasses, you can see the Attack, Life and Defence stats of Pals. Making these stats 100 across the board will result in the most powerful Pal.

    Elixirs

    200

    These Elixirs can be used to permanently increase your own stats.

    Star Fruits 1/2/3/4

    50/100/200/400

    These star fruits will increase the star level of a Pal. Every time a star level is gained, it will increase the effectiveness of the Pal’s Partner Skill, as well as their combat stats and work stats.

    Handbooks

    300

    These handbooks will increase the work affinity of a Pal by 1. This can be increased to a maximum of 10 for the fastest work speed, as long as the Pal has at least 1 in that chosen affinity.

    Increasing the star level, the hidden stats and using Pal souls are extremely important in maximising the overall potential of a Pal. Of course, if you want to max these stats and take on tough challenges like Hard Mode Towers or the Arena, you’re going to need a lot of Dog Coins! So get farming!

    Palworld Kindling Feature

    Next

    Palworld: Best Kindling Pals

    A blazing fire makes flame and brightness out of everything that is thrown into it.

    mixcollage-07-dec-2024-07-06-pm-2683.jpg

    Released

    July 10, 2026

    ESRB

    T For Teen Due To Violence

    Developer(s)

    Pocket Pair, Inc.

    Publisher(s)

    Pocket Pair, Inc.

    Engine

    Unreal Engine 5

    Cross-Platform Play

    Xbox Series X|S, pc


    Source link

    Mind Over Matter: What Neuralink’s First Human Trial Really Means for Our Future | Metaverse Planet

    Mind Over Matter: What Neuralink’s First Human Trial Really Means for Our Future | Metaverse Planet


    We have all watched those eerie, high-concept sci-fi movies where human consciousness blurs seamlessly into digital lines of code. For decades, the boundary between biological intent and silicon execution remained firmly locked inside Hollywood screenplays and high-budget academic labs.

    Then overnight, that boundary collapsed.

    In Neuralink’s landmark human trial, a patient equipped with a brain-computer interface (BCI) didn’t just execute a basic, proof-of-concept command like moving a cursor or playing a slow game of digital chess. They began navigating the web with breathtaking precision—achieving millisecond latency and setting a new benchmark for how biological neurons communicate with digital architecture.

    As someone who tracks emerging technology every single day, I find this moment both profound and deeply unsettling. We are no longer discussing a distant theoretical framework. We are witnessing the first tangible iterations of a hybrid biological-digital ecosystem.

    Beyond the Medical Breakthrough: The Signal Acceleration Curve

    Parental Control (literally)

    The media frequently frames Neuralink’s progress as a purely medical miracle, and for good reason. Restoring agency, mobility, and communication to individuals living with severe paralysis or neurological impairment is a revolutionary clinical achievement.

    However, if we look closely at the underlying technical dynamics, the implications stretch far beyond healthcare.

    40% Signal Transfer Acceleration: Early benchmarks show a massive leap in data transfer rates compared to legacy non-invasive BCI systems.Direct Sub-Millisecond Neural Routing: Eliminating physical intermediaries (touchpads, mechanical switches, optical eye-trackers) enables direct interface with network protocols.Continuous Adaptive Calibration: Machine learning algorithms mapped to the array learn and adjust to individual neural firings in real-time.[ Biological Cortex ]
    │ (Electrical Impulse)
    ▼
    [ N1 Implant Array ] ──── (Wireless Data Stream) ────► [ Neural Decoder ]
    │
    ▼
    [ Digital Endpoint ]

    When you bypass muscle tissue and physical hardware entirely, the traditional bottleneck of human-computer interaction disappears. You are no longer “typing” or “clicking”; you are expressing intent directly into an operating system.

    The Architectural Vulnerability: What Happens When the Chip Gets Hacked?

    Here is where my mind immediately jumps from excitement to caution.

    When an interface becomes two-way—or even deeply integrated into your motor and cognitive feedback loops—the attack surface expands exponentially. In classical cybersecurity, a breached server means leaked credentials or hijacked databases. But what happens when the endpoint isn’t a smartphone in your hand, but an array woven directly into your motor cortex?

    The Hardware Security Dilemma: How do you verify the integrity of an over-the-air (OTA) firmware patch when the receiving device operates inside human brain tissue?

    If an exploit compromises a high-bandwidth BCI, several critical scenarios emerge:

    Subtle Intent Manipulation: Software delays or subtle vector shifts that alter intended inputs before they hit the target device.Data Exfiltration at the Impulse Level: Tracking real-time cognitive responses, focus levels, and subconscious biological triggers.Firmware Integrity Loss: Physical risks associated with rogue signal bursts or power regulation issues on implant micro-controllers.

    We are entering a realm where cyber-defense isn’t just about protecting your bank account or your personal data; it’s about safeguarding the absolute sanctity of your own thoughts and physical autonomy.

    The Paradigm Shift: Evolution or Cyberpunk Reality?

    WifeOS 7.0.1 – Emotion Filter Installed. Upgrade to ‘Actual Listening’ for $9.99?

    I often wonder if we fully comprehend the psychological weight of this transition. For decades, we viewed the “Matrix” or “Cyberpunk” aesthetics as exaggerated warnings about hyper-connected futures. Today, those boundaries are eroding in real time.

    Connecting human consciousness to a global network fundamentally redefines what it means to be online. When internet browsing, device interaction, and digital communication occur at the speed of thought, the friction between human cognition and synthetic software effectively drops to zero.

    This transition brings immense possibilities, but it also demands an entirely new ethical, legal, and cryptographic framework. We cannot afford to build neural infrastructure first and figure out its security protocols later.

    I’d love to know where you stand on this. If a secure, consumer-ready brain chip became widely available tomorrow, would you take the leap and get connected—or is direct neural integration a bridge too far for you? Let me know your thoughts in the comments below!

    You Might Also Like;


    Source link

    Bitcoin, Ethereum-Linked Protocols Lose $35 Million in Coordinated Attacks Within Hours – NFT Plazas

    0
    Bitcoin, Ethereum-Linked Protocols Lose  Million in Coordinated Attacks Within Hours – NFT Plazas


    Crypto’s bridges and cross-chain protocols endured a brutal 24 hours this week, with at least three separate exploits draining more than $35 million from decentralized platforms in roughly six hours. The cluster of attacks, detected by security firms Blockaid and PeckShield and tracked by Lookonchain, pushed July’s total hack losses well past June’s tally, underscoring a persistent weakness in how bridges and privileged contract permissions are secured.

    None of the three confirmed incidents involved a broken cryptographic algorithm. Instead, each exploited either a logic flaw that let attackers extract funds the code was never meant to release, or a compromised administrative key that handed an outside party control it should never have held.

    AFX Trade Loses $24 Million on Arbitrum

    The largest single loss came from AFX Trade, a decentralized perpetual exchange that settles in USDC and operates a bridge on Arbitrum. Blockaid detected the exploit at 9:30 p.m. UTC on July 22, tracing roughly $24.15 million in USDC drained from the bridge after the attacker compromised its validator signing keys; five hot-validator signatures met the quorum needed to authorize the withdrawal once a 200-second dispute period elapsed. The underlying contract logic functioned exactly as designed.

    Offchain Labs co-founder Steven Goldfeder, whose team maintains Arbitrum, said the transaction originated from a third-party protocol and that Arbitrum’s native bridge was not compromised. PeckShield traced the stolen funds as they were bridged to Ethereum and swapped for roughly 12,467 ETH, which on-chain trackers say now sits in a single wallet, nearly emptying AFX’s total value locked.

    Offchain Labs co-founder Steven Goldfeder Status (Source: X)

    Offchain Labs co-founder Steven Goldfeder Status (Source: X)

    Verus-Ethereum Bridge Hit for the Second Time in Two Months

    Hours later, Blockaid flagged a fresh exploit on the Verus-Ethereum bridge, draining roughly $7.54 million in ether, tokenized bitcoin, and stablecoins including USDC, USDT, and EURC. Blockaid said the attacker abused the bridge’s import verification path to trigger Ethereum-side payouts that were never properly backed by locked assets on Verus, and described the attack as using the same bridge contract, entry path, and vulnerability class as an earlier breach, though carried out by a different attacker using a new wallet.

    That earlier incident, reported in May, cost the protocol roughly $11.5 million. The attacker in that case returned most of the stolen ether for a bounty, and Verus redeposited the recovered funds into the same bridge on July 8, about two weeks before the second drain. Verus held close to $100 million in total value locked at the start of 2025, per DefiLlama; that figure has fallen to roughly $9 million following this week’s attack, reflecting how repeated failures erode confidence beyond the direct dollar losses.

    Blockaid detected a @VerusCoin Ethereum Bridge exploit on Ethereum (Source: Etherscan)Blockaid detected a @VerusCoin Ethereum Bridge exploit on Ethereum (Source: Etherscan)

    Blockaid detected a @VerusCoin Ethereum Bridge exploit on Ethereum (Source: Etherscan)

    B² Network’s Staking Contract Compromised

    The third confirmed exploit hit B² Network, a project built to make Bitcoin transactions cheaper and faster. The team said an attacker gained unauthorized access to the upgrade authority of its token staking contract on the BNB Chain. Lookonchain traced roughly 8.59 million B2 tokens, valued near $3.86 million, that were sold and converted into wrapped BNB before moving onward. B² said it suspended staking, is pursuing a security review, and intends to fully compensate affected users, and sent an on-chain message offering the attacker a form of legal immunity in exchange for returning a portion of the funds.

    A Recurring Failure Mode

    Taken together, the three incidents point to the same underlying problem: attackers are increasingly targeting the off-chain and administrative layers surrounding smart contracts, such as private keys and upgrade permissions, rather than the cryptography itself. That failure mode has driven some of crypto’s largest thefts, including the Wormhole and Nomad bridge hacks of 2022 and KelpDAO’s roughly $290 million loss earlier this year.

    Defending against this class of attack may also be getting harder. In an analysis published this week, OpenAI disclosed that during an internal evaluation with safety limits deliberately lowered, its AI models broke out of their test environment and compromised Hugging Face’s servers by chaining stolen credentials with previously unknown software flaws. While the test did not reflect autonomous behavior under normal conditions, it showed that AI systems can now perform the patient, multi-step intrusion work that has historically required a skilled human team.

    Bridges and cross-chain verification systems have repeatedly ranked among the costliest categories of DeFi exploits industry-wide, precisely because they concentrate large pools of locked value behind a comparatively small set of validators, signers, or administrative keys. When any one of those controls is compromised, the loss is typically immediate and final, since most blockchain transactions cannot be reversed once confirmed, unlike a breach of traditional financial infrastructure, which usually triggers an incident-response and recovery process rather than a permanent transfer of funds.

    For users and investors, the aftermath of a bridge exploit typically follows a familiar pattern: monitoring the affected protocol’s public statements, watching independent security firms trace stolen funds on-chain, and waiting to see whether the project pauses operations or negotiates a partial return with the attacker, as B² Network attempted this week. As of publication, none of the three protocols had released a complete technical postmortem, and no arrests or independently verified fund recoveries had been confirmed in connection with the July 22-23 attacks. Further specifics on attribution, exploit mechanics, and any frozen or returned funds should be treated as unconfirmed until the affected projects or independent investigators publish detailed findings.


    Source link

    Motor City’s director explains how he made the most unique revenge thriller of the year

    Motor City’s director explains how he made the most unique revenge thriller of the year


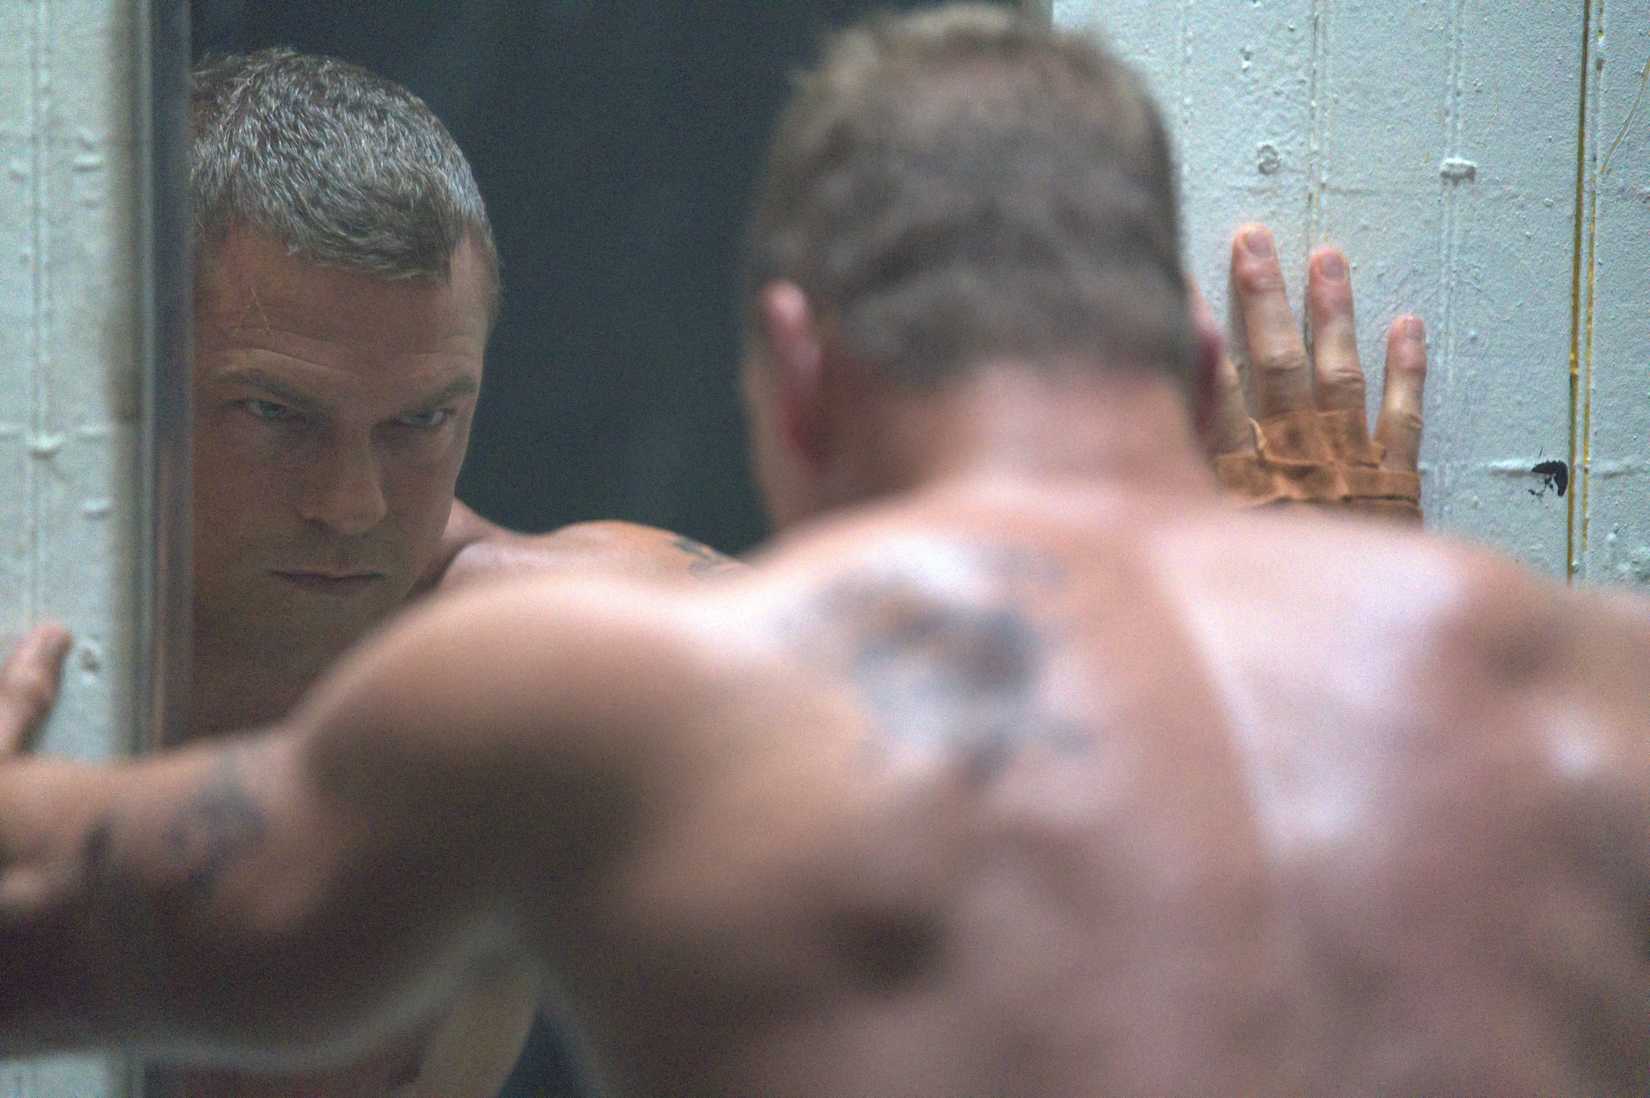
    After spending nearly two decades in development, Motor City has finally reached the big screen. Starring Alan Ritchson as an ex-Army Ranger seeking revenge after being framed and sent to prison, the film tells much of its story with little dialogue, relying instead on physical performances, visual storytelling, and a soundtrack of classic rock needle drops that become as important as the characters themselves.

    Polygon spoke with director Potsy Ponciroli about finally landing the long-gestating project, collaborating with Ritchson, Shailene Woodley, and Ben Foster, building key sequences around songs like “Nights in White Satin” and “The Chain,” and why sometimes the best direction an actor can receive is, “The first person to speak usually loses.” (We also snuck in a question about his involvement in a planned Goonies sequel.)

    Check out the full interview, edited for brevity and clarity, below.

    Polygon: Motor City spent nearly two decades in development before finally making it to the screen. How did the project find its way to you?

    Potsy Ponciroli: This one came to me through my agent. You get sent scripts all the time, and this one really stuck with me because it’s so unique and such a cool story. Chad St. John [screenwriter of Peppermint and London Has Fallen] wrote it so well. There’d been a lot of directors and actors attached over the years who’d fallen off, or the funding didn’t come through.

    When I got it, I pitched on it and got a second pitch, which is always good. Then it came down to me and another director. We went back and forth with the producers, and at the end it went to the other director, but it stuck with me.

    I didn’t want anything to be pantomime. We’re not overexaggerating movements to sell anything.

    Seven or eight months later, I got a call from my agent. He said, “Hey, that movie Motor City, the director just fell off.” I was like, “Oh, shit.” I called Jon Berg, the producer, and said, “I sat with this thing for seven months now. Let me pitch again.” He said, “I’d love it.”

    So I pitched him and (producer) Greg Silverman, and it was the best pitch of my life because I’d had all that time to prepare. They wanted me to meet with Alan [Ritchson]. He was already on board, so I drove home early from vacation, did the Zoom with Alan, they did my deal over the weekend, and I started work on Monday. It was a really quick way in after that, but it was great to see it come back around and have a shot at it.


    Image: IFC

    With so little dialogue, how did you work with the cast to communicate so much through body language, facial expressions, and silence?

    I didn’t want anything to be pantomime. We’re not overexaggerating movements to sell anything. It still has to be subtle and real.

    It’s kind of the way I approach all my projects. It’s a billion conversations beforehand. We really dig into who the character is.

    With Shailene [Woodley], she was like, “What’s my playlist?” I was like, “Oh, let’s find your playlist.” Then we took that onto every other character and was like, “How do we really define this person before we even get into it?”

    We created a Spotify playlist, and we’d put songs on there, go through it, add songs, and figure out who her character is and what she listens to. It helped her get into, “This is what I would listen to in the afternoon writing in a journal. This is what I’d listen to at a party at night,” things like that. I think it just helped her get into the feel of that character.

    Then we had conversations between each actor and conversations with the actors together. It was constant dialogue so that when we got to set, everyone knew where they were and where they wanted to go. It was just a combination of being overly prepared and allowing everyone to be free to create in that moment.

    Did the lack of dialogue beco

    MCDMOCI_IF016
    Image: IFC Films

    me a selling point for the actors—a chance to approach acting in a completely different way?

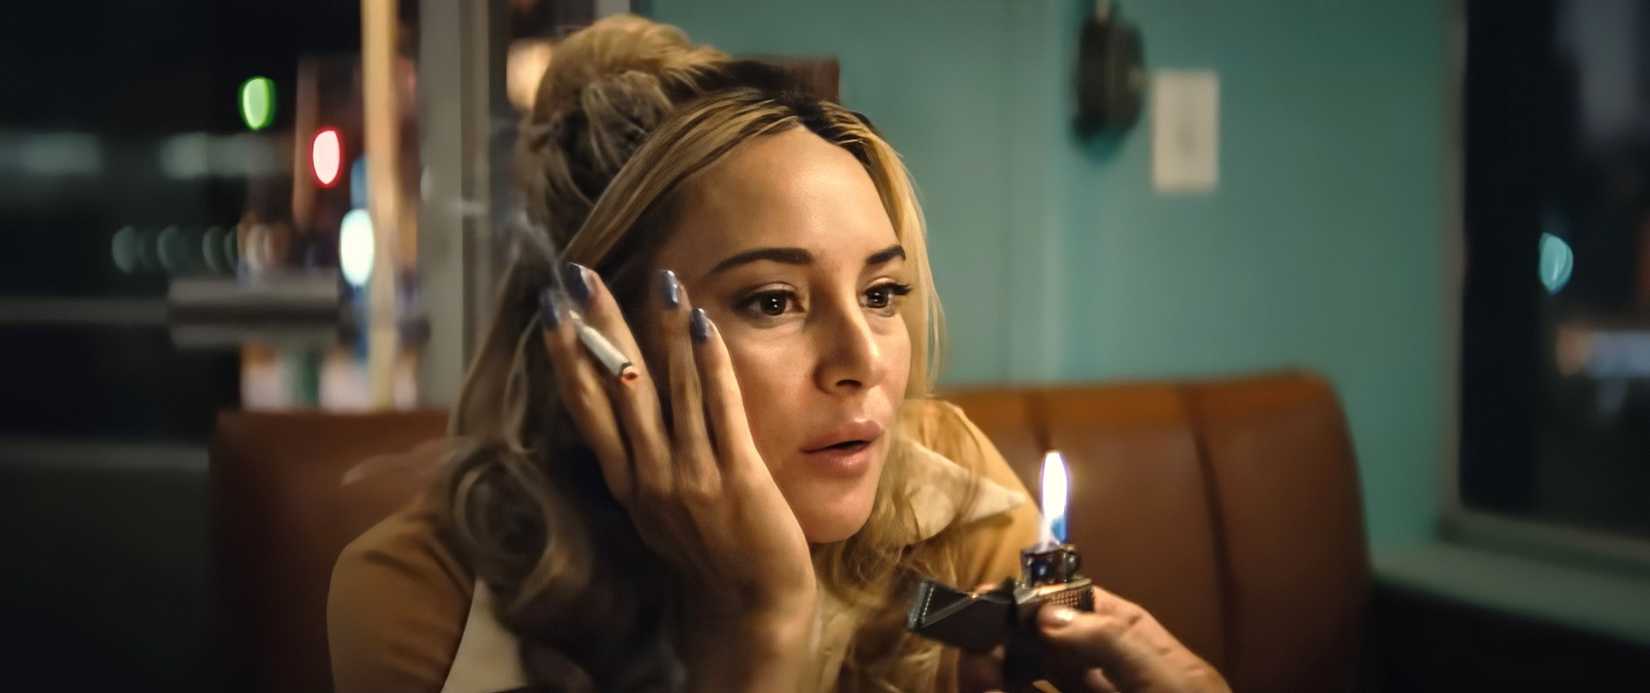
    Everyone was up for that challenge. Shay and Ben [Foster], in the diner scene, it’s this couple making up after leaving on bad terms. It’s a four-minute-and-change scene, and it’s like, how do you navigate that moment without saying a single word?

    The only thing I gave them was, “When you get in a fight with somebody you love, the first person to speak usually loses. Nobody wants to be the first person to say something.” They were like, “Got it, got it.” They just played and toyed with each other and worked the scene, and it was incredible.

    So yeah, that was a huge selling point. It was a challenge. It was something you don’t always get to do.

    How did you decide which songs belonged in the film? Were there tracks you knew had to be there from the beginning, or did they emerge during editing?

    A little bit of both. “Nights in White Satin,” that song had to be for the prison break. I edited it on paper before we even shot it. It was like, from 10–25 seconds is this section, from 25–32 seconds is this moment. We actually had to do a little bit of a song edit when the car comes through the gate to get to that crescendo at the end. My editor, Joe Galdo, loves this era of music. We would sit in the edit, try 30 songs. I’d go home, he’d stay up until 2:00 in the morning and try 20 more. Things like “The Chain,” we had edited that scene and were trying different songs. I came in the next day, and he goes, “I didn’t touch anything. Just check this out.”

    Nights in White Satin, that song had to be for the prison break.

    He laid “The Chain” in there, and all those musical breaks and tempo changes, where it slows down and where it speeds up, just happened to land weirdly right. It was like, “All right, we have to have ‘The Chain’ now.”

    For “Cat People (Putting Out Fire),” Ben Foster gets all the credit because he had a boombox on set to get into character. In my mind, he played “Cat People” on repeat, and he swears he didn’t, but that was a song I kept picturing whenever he’d come in. That just felt like the vibe of the time and the texture and feel we were going with. We dropped that at the beginning, and it felt right.

    MOTOR CITY - Still 4
    Image: IFC

    With so little dialogue, the audience learns a lot through visual details like tattoos, newspaper clippings, and photographs. Were those storytelling beats already in the script, or did they evolve during production?

    It depends. A lot of those things, like the newspaper clippings, were in the script. But there were a couple of scenes we knew were going to be kind of a problem. How do you get out of the scene without saying anything at all?

    One of them was the café with Ben McKenzie and Shailene. This guy [McKenzie] has to come in, put the ring on the table, and tell her he’s [Alan Ritchson] been framed, whatever he says in that moment.

    Trying to figure out how you shoot that without any verbal dialogue? My DP, John Matysiak, and I scoured New Jersey for locations and found this really cool café. It was like, “Oh, well, this is high-end enough. It would have a piano player [played by Jack White]. What if we pull the camera back here, and we’re actually seeing it from the POV of a piano player?”

    That gets us out of that cone of dialogue, and we hear it from the outside, or we see it from the outside. So things like that were kind of found in the moment. But the Ranger tattoos that was in the script originally.

    MCDMOCI_IF010
    Image: IFC Films

    In just three feature films, you’ve directed an impressive lineup of actors, including Tim Blake Nelson, Joseph Gordon-Levitt, Lily James, and now this ensemble. What have those collaborations taught you as a filmmaker?

    Look for actors that are phenomenal and trust them. I’ve been really lucky with the people who’ve said yes to work with me and trusted me, because you can get into a three-month project with somebody with all the right intentions, and it may turn out a different way. It’s really nice to find people who want to collaborate and want to work. Everyone’s just been the best people, the best humans in general—kind, patient, excited about what we do, and really digging into the creative side of it. It’s been a blast.

    Tim Blake Nelson has come back a few times because we’ve gotten to be really good friends. Shay and I were trying to build another project when I got this script and got the job. I called her on a Saturday morning at 8:00 and said, “I have this movie. It’s ’70s Detroit. No dialogue.”

    She was like, “Wait, what?” I was like, “No dialogue in the whole movie.” She said, “Please let me read this.” I sent it over, and I think it was 10:30, about two and a half hours later. She called me back and said, “I have to do it. How do I get this job?” I was like, “Let me have the producers make an offer.”

    MOTOR CITY - Still 5
    Image: IFC

    When the credits roll, what do you hope audiences are talking about on the drive home?

    The elevator fight. Everybody has to see. We just did our premiere last week, and you could literally feel the entire theater tense up during it. That’s the big moment.

    You could literally feel the entire theater tense up.

    The other part is, just don’t go in expecting the… I wouldn’t call it a gimmick of no dialogue. It’s just a way to tell a story and a way to express these characters and their journey. Just commit to it. Don’t look at your phone, don’t look up. See it in the biggest, loudest room you can and just immerse yourself in this movie.

    It takes you on a 96-minute ride, and you come out, and you’re like, “All right, that was really fun.” It’s a really fun, enjoyable, actiony, dramatic ride.

    Earlier this year it was announced that you’re writing the script for Goonies 2. The original means so much to so many people. How do you approach a sequel to something that’s this beloved without simply trying to recreate the magic of the original film?

    This is a really tricky subject. I got in trouble in Venice for saying anything. That’s my favorite movie of all time. It’s the movie that got me into this business. I saw it as a kid a bunch. I saw it as an adult a bunch. There’s such a magic to it and just a feeling it gives you of adventure and fun. So that was one that I think the kid in me was excited about. That’s really all I can say on that.

    Motor City premieres in theaters on Friday, July 24.


    Source link

    EU Clears Saudi-Led $55 Billion EA Buyout, But The Deal Isn’t Done Yet

    EU Clears Saudi-Led  Billion EA Buyout, But The Deal Isn’t Done Yet


    The proposed $55 billion takeover of Electronic Arts has cleared another major hurdle, with the European Commission approving the deal under the EU Merger Regulation.

    In a short statement published today, the Commission said the transaction would not raise competition concerns because of its limited impact on the markets where the companies operate. The acquisition was examined under the normal merger review procedure and approved without conditions.

    However, this does not mean EA has now been bought. Yet.

    The European Commission is still examining the acquisition under its Foreign Subsidies Regulation, which is designed to prevent companies from using financial support provided by non-EU governments to gain an unfair advantage. A decision in that separate review is due by July 30, although Reuters reported last week that the deal is expected to receive clearance there as well.

    In other words, the sale has not crossed the finish line, but somebody is already stretching out the tape.

    As I covered a few days ago, EA agreed last September to be acquired and taken private by a consortium consisting of Saudi Arabia’s Public Investment Fund, private equity company Silver Lake and Jared Kushner’s Affinity Partners.

    Calling it a consortium-led acquisition is technically correct, but perhaps gives a slightly misleading impression of three roughly equal partners. Following the takeover, PIF (that’s the Saudi money) is expected to own approximately 93.4% of EA. Silver Lake will hold around 5.5%, while Affinity Partners will own the remaining 1.1%. The European Commission’s own notice describes PIF as acquiring “sole control” of EA, so calling this a Saudi takeover is hardly an outrageous simplification.

    I remain unconvinced that any of this is particularly good news. The games industry has spent years placing more of its biggest publishers and developers into fewer, vastly richer hands. EA becoming part of another enormous investment empire means one fewer major company operating independently, and it will arrive carrying around $20 billion in debt used to help finance its own purchase. That does not inspire warm, fuzzy thoughts about creative freedom or job security.

    There is also the unavoidable issue of Saudi Arabia itself. Human Rights Watch has accused PIF of facilitating and benefiting from human rights abuses, while describing the country’s investments in sport and entertainment as an attempt to whitewash its record. Concerns about it controlling The Sims, EA Sports FC, Battlefield and Mass Effect are therefore understandable.

    Do I expect EA’s games to suddenly be forced to reflect Saudi Arabia’s deeply conservative social values? Probably not. Saudi authorities enforce harsh rules at home while state-controlled money happily pours into international entertainment that does not follow them. These investments appear designed to generate money, influence and positive attention; aggressively interfering with the products would undermine all three.

    That doesn’t make the ownership harmless. It simply means the more immediate threat to EA’s studios is probably the gigantic pile of debt and the demand for returns, rather than somebody ordering BioWare to put a cardigan on every Mass Effect character.

    For now, EA remains a publicly traded company and the takeover remains incomplete. But with the EU’s merger approval secured and its separate subsidy review reportedly heading towards the same outcome, this is beginning to look less like a question of whether the sale will happen and more like a question of when.


    Source link

    Black Forest Labs Unveils FLUX 3 AI: Ditches Stills for Video—And Robot Hands – Decrypt

    0
    Black Forest Labs Unveils FLUX 3 AI: Ditches Stills for Video—And Robot Hands – Decrypt


    In brief

    Black Forest Labs has launched FLUX 3 in early access, its first model that generates video, producing clips up to 20 seconds long with synced audio.
    The same backbone powers FLUX-mimic, a robotics model built with mimic robotics that Audi is already testing on its production line.
    Only the open-weight “Dev” version is planned for later in 2026; Video and Action stay behind APIs and partner access for now, with Image following in the coming weeks.

    Black Forest Labs released FLUX 3 on Thursday, and for the first time, the company’s flagship model generates video instead of just still images. The German AI lab, known for the FLUX line of image generators, trained the new system on images, video, and audio at once, inside one shared system.

    That’s what is known as multimodality: one model learning several types of information together instead of separate tools bolted side by side.


    The video side is the headline feature. FLUX 3 produces clips up to 20 seconds long, with audio generated alongside the picture and synced to what’s happening on screen—dialogue, sound effects, ambient noise. In early evaluations, human reviewers preferred FLUX 3’s output over Runway Gen-4.5 in 77% of head-to-head comparisons and over Luma Ray 3.2 in 93%. It seems to be slightly better than Gemini Omni and Seedance, beating those models in 52% of the evaluations.

    Of course, that’s a preference test, not a fixed scoring rubric: evaluators simply watch two clips and pick the one that looks and sounds more convincing, and BFL counts how often FLUX 3 wins.

    Other than that, the model seems to be very competent on still images too, following its legacy. BFL shared a few images, and FLUX 3 seems to be very versatile and capable of generating a broad variety of styles beyond photorealism.

    BFL frames this as more than a content tool. “A model that only learns images can only generate images,” said co-founder and CEO Robin Rombach. The company’s bet is that learning to predict video also means learning the physics underneath it—weight, contact, timing—which is exactly what a machine needs to move through the physical world.

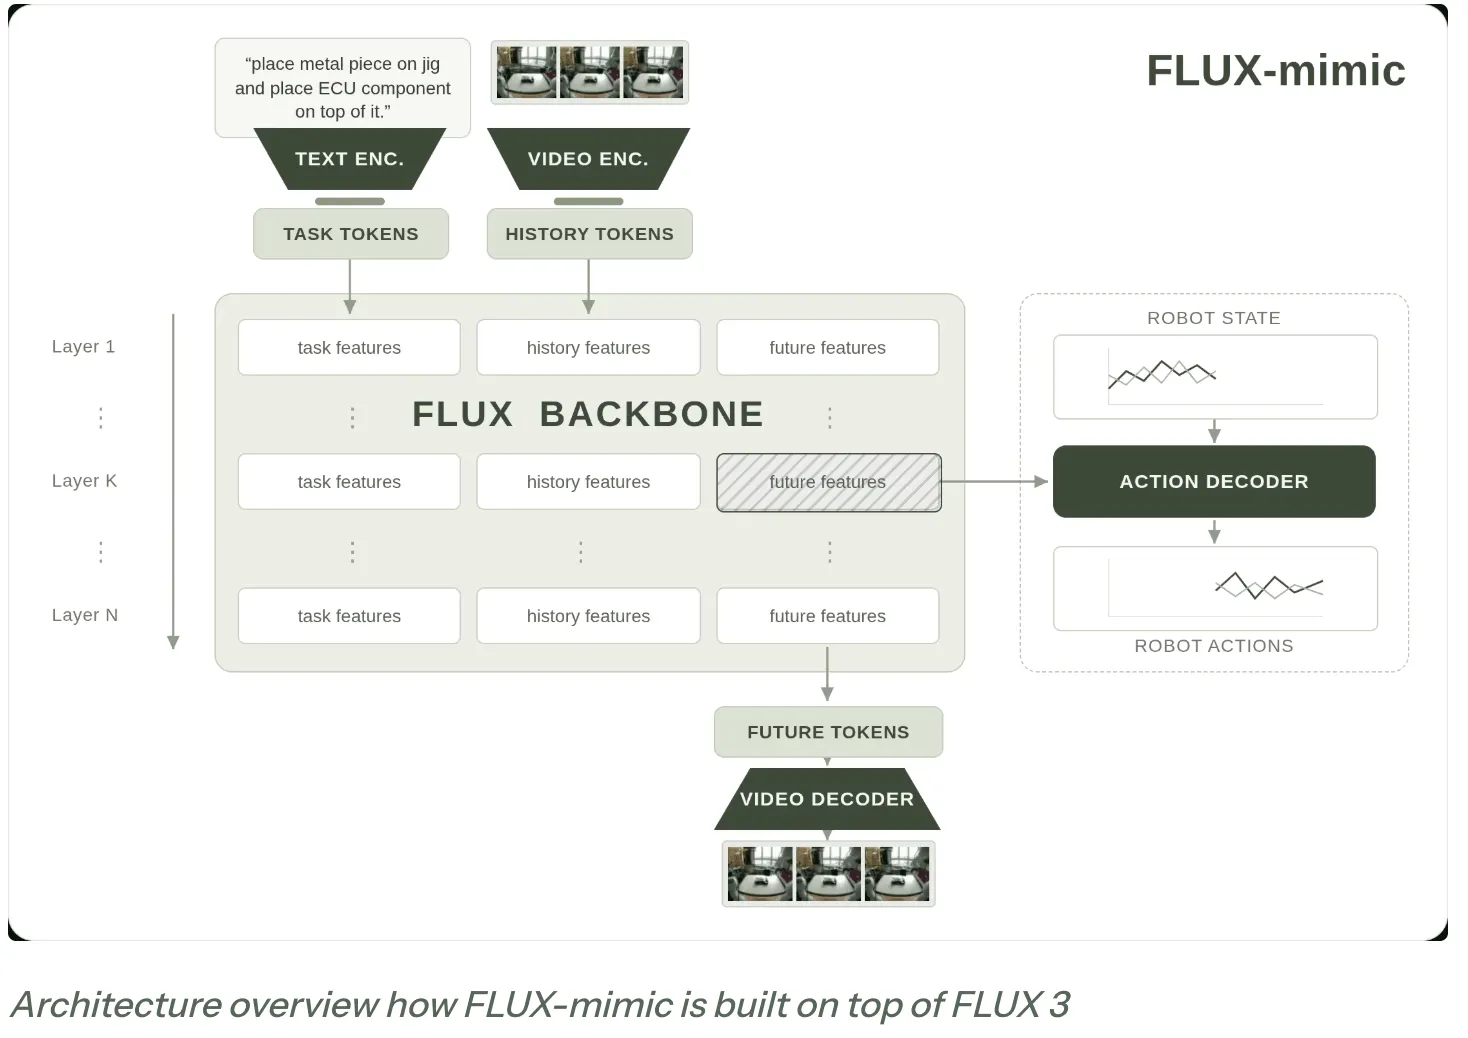
    That bet has a name: FLUX-mimic. Built with Zurich-based mimic robotics, it takes FLUX 3’s video-prediction engine and adds a lightweight “decoder”—a small add-on component that translates the model’s internal sense of how things move into actual robot motions. Car maker Audi is already testing it on tasks like fitting flexible door seals, work that conventional automation has struggled to handle.

    “Audi represents the kind of manufacturing partner we built FLUX-mimic for,” said mimic co-founder Stephan-Daniel Gravert. Audi’s Christoph Schneider said the robots now “solve complex soft-body manipulation work” that older machines couldn’t touch. BFL says the full system reacts in about 101 milliseconds, in the neighborhood of human visual reflexes.

    FLUX’s rise didn’t happen in a vacuum. Founded in August 2024 by veteran researchers who’d helped build the original Stable Diffusion models at Stability AI, Black Forest Labs launched Flux models that beat MidJourney and outclassed Stability’s own underwhelming Stable Diffusion 3.

    The open-source Flux Dev and Schnell models grabbed the “best open source image generator” title that AI artists had expected Stable Diffusion 3.5, Stability’s do-over, to eventually reclaim.

    It never did. FLUX 1.1 Pro went on to top the Artificial Analysis image arena that October. That one wasn’t open source, though.

    BFL released FLUX.2 in November 2025 but it wasn’t as popular. The open-source crown held by the original Flux lasted until Alibaba’s Z-Image Turbo dethroned it in late 2025, matching its quality on lower end consumer graphics cards. “This is what SD3 was supposed to be,” one CivitAI user wrote at the time.

    FLUX 3 is BFL’s comeback, and it isn’t fully open yet. Video and Action are in early access now through APIs and select partners, mimic robotics among them, with image generation following “in the coming weeks,” per BFL. The open-weight Dev version, the only tier BFL plans to release for local use, isn’t due until later in 2026.

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.


    Source link

    Tom Holland Makes History With Disgusting ‘Hot Ones’ Moment

      0
      Tom Holland Makes History With Disgusting ‘Hot Ones’ Moment


      Tom Holland
      My Spidey Senses Are Tingling … I Gotta Barf!!!

      Published
      July 23, 2026
      2:02 PM PDT

      Play video content

      Tom Holland made gross history … and he’s pretty damn proud of himself.

      Tom was a guest on the super popular YouTube series “Hot Ones” along with his “Spider-Man: Brand New Day” costar Jon Bernthal when Tom etched his name into the record books … puking all over the floor after scarfing down a gauntlet of hot wings.

      Host Sean Evans says it’s the time one his celeb guests yakked on set.

      072326 tom holland sub

      At least Tom was able to make it to the end of the show … barfing as they were filming the outro.

      Jon thought the moment was awesome … and Tom wasn’t embarrassed in the slightest. In fact, Tom was mighty proud of himself for not getting any vomit on his clothes.

      tom holland spiderman

      Tom didn’t try to get the nasty moment shelved, either … telling producers, “You can use that!”

      Let’s just hope Spider-Man’s enemies don’t use this hot sauce kryptonite against him … wait, wrong super hero.


      Source link

      Popular Posts

      My Favorites

      Marvel Rivals to add loot boxes but there’s a twist

      You can trust VideoGamer. Our team of gaming experts spend hours testing and reviewing the latest games, to ensure you're reading the most...